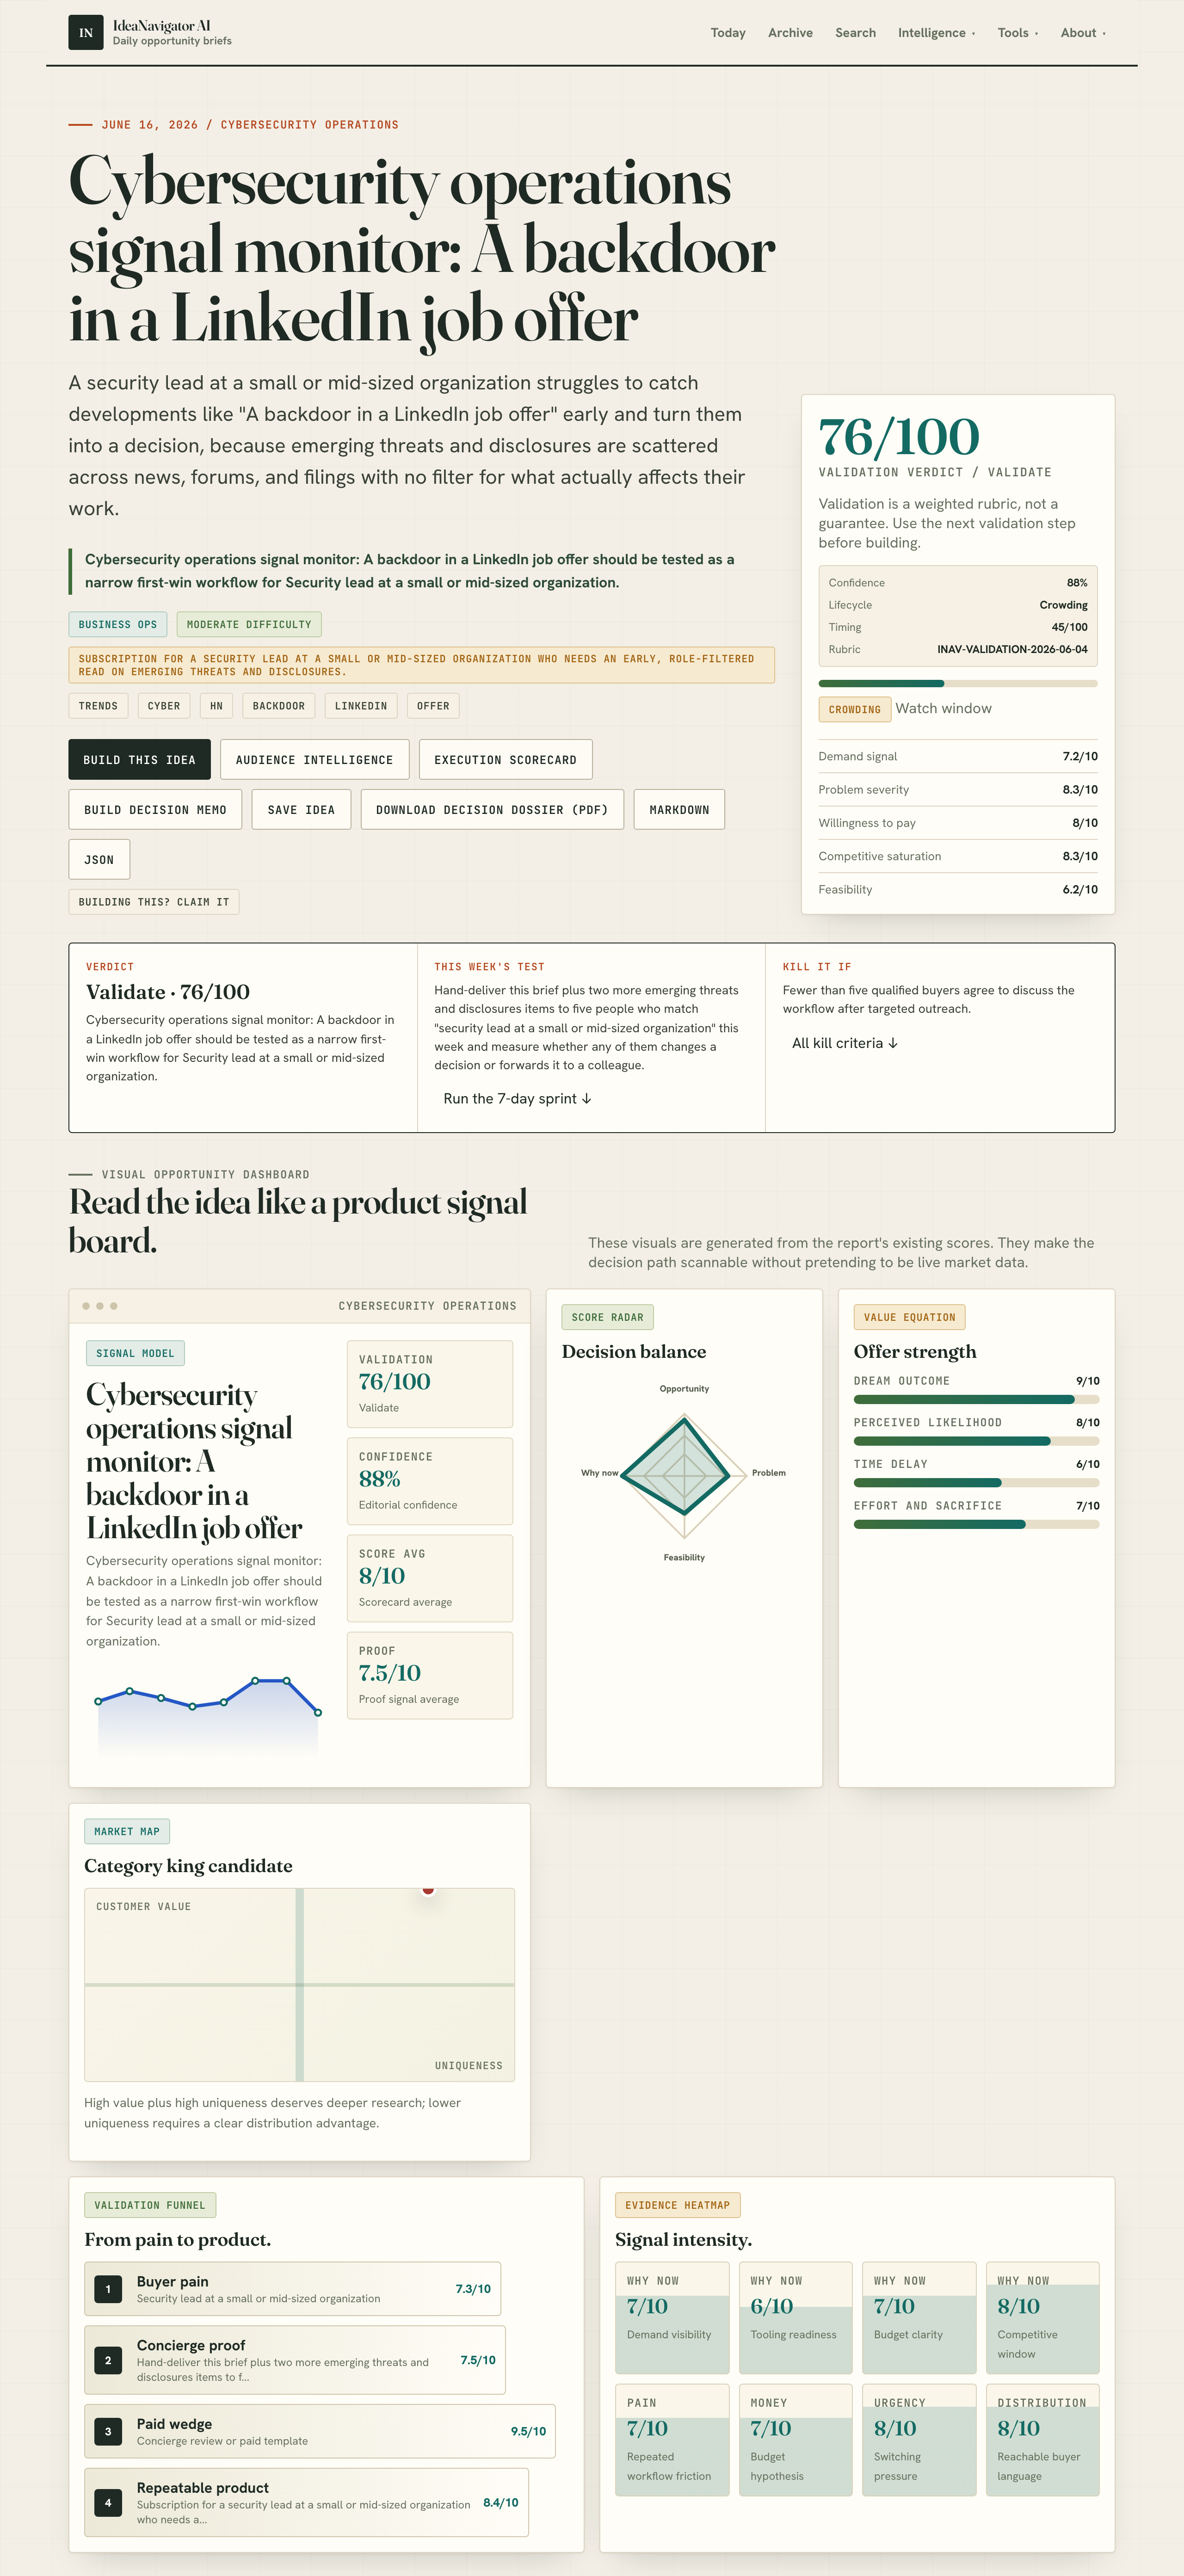
📊 Full opportunity report: Uncovering Backdoors In Cybersecurity Operations: A LinkedIn Job Offer Trap on IdeaNavigator AI — validation score, market gap, and execution plan.

Get smart everyday buys delivered free — and shop member deals
- Fast, free delivery on millions of items
- Access to Prime Big Deal Days deals on October 6–7
- Prime Video, Amazon Music and more included
TL;DR
Security researchers have identified a method where malicious actors embed backdoors in LinkedIn job offers. This development signals a new vector for cyber attacks, prompting alerts for security teams. The full scope and impact are still being investigated.
A recent cybersecurity alert has uncovered a method by which malicious actors embed backdoors into LinkedIn job postings, posing a new threat to organizations’ security defenses. This development is significant for security leads at small and mid-sized firms, as it highlights a potential entry point for cyber attacks that may bypass traditional defenses.
Cybersecurity researchers have identified instances where cybercriminals insert malicious code into LinkedIn job offers, creating backdoors that could be exploited once a candidate or recruiter interacts with the posting. The technique involves embedding malicious scripts or payloads within the job description or application links, which can activate when viewed or clicked.
These backdoors could allow attackers to gain unauthorized access to internal networks or deploy malware once the malicious link or script is executed, potentially compromising sensitive organizational data. The threat was highlighted after a series of reports on Hacker News, which scored an 88/100 signal, indicating a rising concern among cybersecurity professionals.
While the exact scope and scale of this method are still under investigation, early evidence suggests that it is being used in targeted campaigns against small and mid-sized organizations, which often lack advanced threat detection capabilities. Experts recommend vigilance in scrutinizing job postings and related application links for unusual activity or code.
Potential Impact on Small and Mid-Sized Organizations
This development underscores a new attack vector that could bypass traditional perimeter defenses, especially in organizations with limited cybersecurity resources. If exploited successfully, these backdoors could lead to data breaches, ransomware infections, or lateral movement within corporate networks.
Security leads must now consider social engineering combined with technical exploits in job recruitment channels, which are typically trusted platforms. Early detection and awareness are crucial to prevent malicious entry points from being exploited.
cybersecurity threat detection tools
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Emerging Threats in Cybersecurity Recruitment Channels
Over recent months, cybercriminals have increasingly targeted social media and professional networking sites, exploiting their trust and widespread use. The recent alert about backdoors in LinkedIn job offers follows a pattern of emerging threats that leverage legitimate platforms for malicious purposes.
Historically, attackers have used phishing emails and malicious attachments; now, embedding malicious code directly into job postings represents an evolution in attack strategies. This trend emphasizes the need for organizations to adapt their threat detection to include social media and recruitment channels.
“Embedding backdoors in LinkedIn job offers is a new frontier for cybercriminals, and organizations must be vigilant in scrutinizing these postings.”
— an anonymous cybersecurity researcher
As an affiliate, we earn on qualifying purchases.
Scope and Exploitation Level of the Backdoor Technique
It is not yet clear how widespread the use of backdoors in LinkedIn job offers is or whether this technique has been widely exploited in active campaigns. Details about specific payloads, targeted industries, or successful breaches remain under investigation.
Security experts are still assessing whether this is a limited tactic or part of a broader, coordinated effort among threat actors.
network security monitoring devices
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Monitoring and Response Strategies for Organizations
Security teams are advised to increase vigilance by scrutinizing job postings and application links for unusual activity. Developing automated filters or manual review processes for suspicious content can help detect potential backdoors early.
Further investigations are expected to clarify the scope of the threat, and organizations should stay updated on advisories from cybersecurity authorities. Implementing user awareness training about social engineering risks linked to recruitment channels is also recommended.
As an affiliate, we earn on qualifying purchases.
Key Questions
How can organizations detect backdoors in LinkedIn job offers?
Organizations should scrutinize job postings for unusual scripts, links, or code snippets embedded within descriptions or application URLs. Using security tools that scan links and embedded content can help identify malicious payloads.
What are the risks if a backdoor in a LinkedIn job offer is exploited?
If exploited, attackers could gain unauthorized access to internal networks, deploy malware, or steal sensitive data. This could lead to data breaches, operational disruptions, or further infiltration.
Are all LinkedIn job offers potentially dangerous?
No, most legitimate job postings are safe. The concern is with postings that contain suspicious links or embedded code, which require careful review and verification.
What should security teams do immediately after learning about this threat?
Teams should increase monitoring of recruitment channels, educate staff about social engineering risks, and implement filters to detect suspicious content. Reporting any suspicious postings to platform administrators is also recommended.
Will this threat likely increase in the future?
Given the evolving tactics of cybercriminals and the attractiveness of social engineering, it is likely that similar methods will become more prevalent unless defenses are strengthened.
Source: IdeaNavigator AI
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.