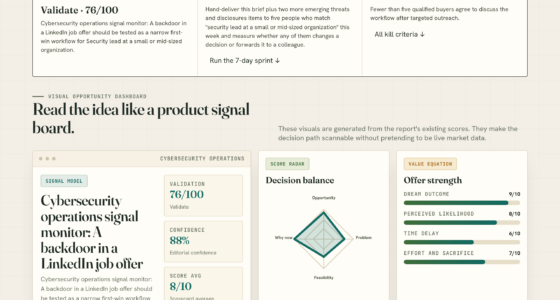
📊 Full opportunity report: Device Security Checker For Remote Teams' Mixed Hardware on IdeaNavigator AI — validation score, market gap, and execution plan.
Prime for Young Adults — start your free trial
Fast free delivery, streaming and member deals for eligible 18–24 year olds.
Try it freeAs an affiliate, we earn on qualifying purchases.
TL;DR
A startup has introduced a device security checker designed for remote teams with diverse, employee-owned hardware. The tool verifies encryption, OS updates, and screen locks, reporting compliance status without invasive management. Its initial deployment targets SMBs preparing for security audits.
A new lightweight device security checker has been introduced to help remote teams with mixed hardware verify their security posture. The tool, designed for operations or security leads at SMBs, is a voluntary agent that checks device encryption, OS updates, screen locks, and password management, reporting results without remote control capabilities. This development responds to increasing compliance demands from frameworks like SOC 2 and the limitations of traditional MDM solutions for employee-owned devices.
The security checker is intended as a minimal, easy-to-deploy solution that provides clear pass/fail reports on device security status. Employees install the agent voluntarily, and it assesses critical security features such as disk encryption, OS patch levels, screen lock settings, and password manager presence. The tool then reports the results to a centralized dashboard accessible by security teams, along with self-remediation instructions for non-compliant devices. The approach avoids invasive remote control, aligning with employee privacy concerns and the typically unmanaged nature of personal devices.
This initial product concept aims to serve SMBs facing increasing security and compliance requirements, especially as SOC 2 audits become more common across organizations of all sizes. The company plans to monetize via per-device monthly pricing, with additional features such as compliance report exports available on paid tiers. The tool’s simplicity and focus on voluntary installation aim to facilitate quick adoption and ease of use, especially among remote teams with diverse hardware setups.
Early validation involves deploying the checker at ten remote startups preparing for SOC 2 audits, with success measured by device enrollment rates and acceptance of the compliance reports by auditors. The goal is to demonstrate that the tool can reliably verify security postures and serve as evidence during formal assessments, filling a critical verification gap for employee-owned devices.
Why a Lightweight Security Check Is Critical for SMBs
As remote work becomes the norm, SMBs face increasing pressure to demonstrate security compliance, especially under frameworks like SOC 2. Traditional management tools such as mobile device management (MDM) are often too invasive or impractical for employee-owned devices, leaving a verification gap that could jeopardize audits and customer trust. The new device security checker offers a non-intrusive, scalable solution that enables organizations to verify essential security controls quickly and efficiently. By automating checks on encryption, updates, and screen locks, the tool helps SMBs reduce compliance risks, avoid breaches, and build confidence with auditors and customers. Its focus on voluntary employee participation also respects privacy concerns, making it more likely to be adopted at scale.
device security compliance checker
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Growing Need for Device Security Verification in Remote Work
The rise of remote work has led to a proliferation of employee-owned devices used for work, including Macs, Windows laptops, and unmanaged smartphones. This diversity complicates security management, as IT teams lack visibility into whether devices meet basic security standards such as disk encryption, OS patching, and screen lock activation. Traditionally, SMBs have relied on heavyweight mobile device management (MDM) solutions, which often require device enrollment and can be perceived as invasive or burdensome, especially for personal devices. Meanwhile, compliance frameworks like SOC 2 increasingly demand documented verification of security controls, but existing solutions are not well-suited for unmanaged, personal hardware.
In response, some companies have explored lightweight agents or manual questionnaires, but these approaches are often cumbersome, unreliable, or easily bypassed. The new security checker aims to fill this gap by providing a simple, voluntary, and automated verification process that can be integrated into existing workflows. Early pilot programs are underway, with a focus on demonstrating that the tool can be accepted by auditors and effectively improve security posture reporting for SMBs facing compliance deadlines.
remote device security verification tool
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Unanswered Questions About Deployment and Auditor Acceptance
It is not yet clear how quickly SMBs will adopt the voluntary agent at scale or whether organizations will face resistance from employees concerned about privacy or device control. Additionally, the acceptance of the generated compliance reports by auditors remains unconfirmed; validation depends on early pilot results and feedback from security auditors involved in SOC 2 assessments. The long-term effectiveness of the tool in preventing breaches or uncovering non-compliance in diverse hardware environments also remains to be demonstrated through broader deployment.
employee device encryption checker
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Next Steps for Deployment and Validation in SMBs
The company plans to launch pilot programs with ten remote startups over the next few months, focusing on measuring device enrollment rates and auditor acceptance of reports. Success metrics include high voluntary installation rates, positive feedback from security teams, and formal recognition of the reports during audits. If successful, the product could expand to larger organizations and integrate with existing security workflows. Further development may include adding features such as automated remediation guidance and integration with other security tools to enhance overall device posture management.
As an affiliate, we earn on qualifying purchases.
Key Questions
How does the device security checker work without remote control?
The agent runs locally on the device, performing security checks such as encryption status and OS updates, then reports the results to a centralized dashboard. It does not have remote control capabilities, respecting employee privacy and device autonomy.
Is this tool suitable for personal devices used for work?
Yes, the tool is designed as a voluntary, lightweight agent that employees can install on personal devices, making it suitable for unmanaged, employee-owned hardware used for work purposes.
Will the reports be accepted by auditors for compliance purposes?
Acceptance depends on validation during pilot deployments. Early efforts aim to demonstrate that the reports meet auditor standards for verifying device security controls during SOC 2 assessments.
What security features does the agent verify?
The agent checks for disk encryption, OS update status, screen lock activation, and the presence of password managers, providing a pass/fail report for each.
How is this product priced?
The initial business model involves per-device monthly pricing, with additional features such as compliance report exports available on paid tiers.
Source: IdeaNavigator AI
Fall yard work Picks
leaf blowers
As an affiliate, we earn on qualifying purchases.